Secure Software Development — Ship Fast, Stay Audit-Ready
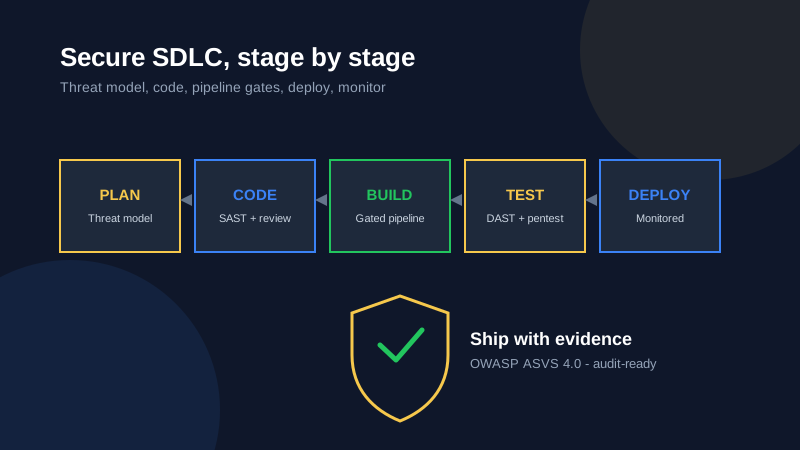
Application flaws cause the majority of enterprise breaches, and fixing them in production costs up to 30x more than catching them in design. We embed security into your SDLC so release velocity holds and every release ships with evidence your auditors accept.
Business outcomes
- Fewer production incidents — clients typically cut release findings by 60-70 percent within two quarters.
- Faster audit sign-off — an OWASP ASVS 4.0 evidence pack that satisfies ISO 27001, SOC 2, and enterprise customer security reviews.
- Velocity preserved — guardrails run inside your pipeline; developers receive fix guidance, not blocking tickets.
What we deliver
- Threat modeling and secure design review — STRIDE-based workshops per major feature; risks are logged before code exists.
- Code assurance — SAST and SCA tuned to your stack, plus expert manual review for the logic flaws tools miss.
- Pipeline gates — SAST, DAST, SCA, and secret scanning wired into GitLab, GitHub, or Jenkins with fail-fast feedback.
- Container and IaC hardening — image baselines, Kubernetes and Terraform checks, and dependency monitoring.
- Developer enablement — secure-coding coaching and playbooks so your team depends on us less over time.
Compliance mapping
| Framework | How we map |
|---|---|
| OWASP ASVS 4.0 | Verification levels per release |
| NIST SSDF | Secure development practices |
| ISO 27001:2022 | Clause A.8 secure engineering evidence |
Engagement models
| Model | Best for | Typical duration |
|---|---|---|
| Embedded AppSec squad | Continuous delivery teams | Quarterly |
| Pipeline uplift | Toolchain with no gates yet | 4-6 weeks |
| Assessment and roadmap | Planning next fiscal year | 2-3 weeks |
Start with a scoping workshop
A free 90-minute session maps your stack, top risks, and the smallest high-value first step. Talk to sales — 24-hour response, NDA on request.