Cybersecurity Assurance — Evidence Your Board and Auditors Trust
Every CISO must answer three questions: can we withstand a real attack, will the auditor say yes, and where should the next budget go. Our assurance practice answers all three with tested evidence — not checklist scans.
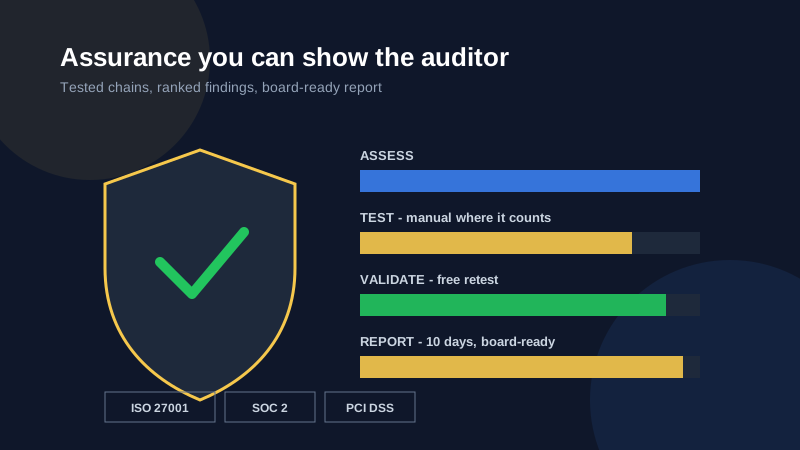
Business outcomes
- Audit-ready evidence — findings mapped to ISO 27001, SOC 2, PCI DSS, and regulator expectations, accepted by enterprise customers.
- Risk you can prioritize — every finding ranked by real exploitability with a kill-chain narrative, so remediation budgets land where they matter.
- Measurable reduction — most clients cut critical findings by around 80 percent after the included free retest.
What we deliver
- Penetration testing — external, internal, API, cloud, and mobile. Manual testing where it counts: chained attack paths, not CVE dumps.
- Red team exercises — adversary simulation across people, process, and technology, measured against your SOC detection time.
- Vulnerability management — continuous discovery with noise removed and Jira-ready tickets your engineers will actually close.
- Source code review — SAST plus expert manual review for business-logic flaws automated tools cannot see.
- Social engineering — quantified phishing assessments with click rates, affected groups, and targeted remediation.
Deliverables
Board-ready report within 10 days, executive summary plus full technical findings, free retest to prove closure, and NDA protection on every engagement.
Compliance mapping
| Framework | How we map |
|---|---|
| ISO 27001:2022 | Control testing evidence |
| SOC 2 | Trust criteria validation |
| PCI DSS | Requirement 11 testing support |
| NIST CSF | Identify, Protect, Detect coverage |
Start with a scoping workshop
A free 90-minute session defines scope, rules of engagement, and fixed pricing. Talk to sales — 24-hour response, NDA on request.